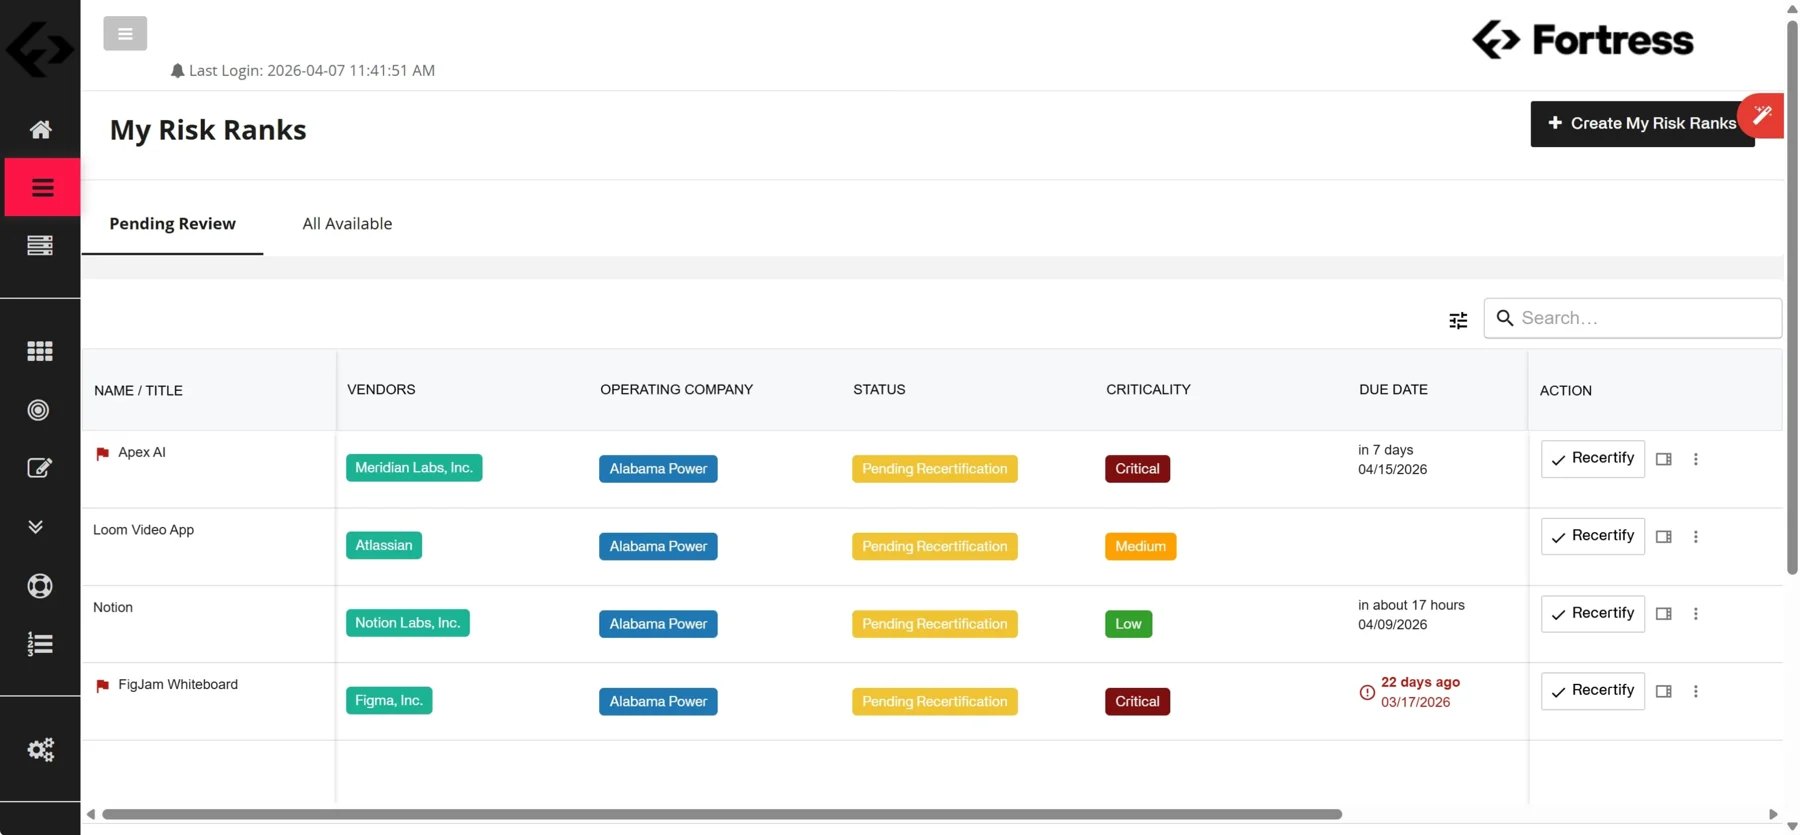
A Fortress client who actively leverages Software Bill of Materials (SBOMs) and Data Driven Product Assessments (DDPAs) was experiencing delays in receiving vendor files required to complete SBOM reviews. To stay on track with internal service level commitments, the client refined their workflow to automatically convert an SBOM request into a DDPA if the necessary file is not received within 48 hours.
SBOM reviews depend on timely delivery of vendor provided component lists. When those files arrive late, or not at all, review queues stall, and teams risk missing SLA timelines. The client needed a way to preserve decision grades without being gated by supplier response times.
The client instituted a 48-hour escalation rule: if an SBOM file hasn't been received within two business days, the request auto converts to a DDPA. DDPAs provide rapid, open source, product level risk intelligence, evaluating ~65 security controls across categories such as vulnerability response, patching cadence, and disclosure processes—delivered on a short turnaround.
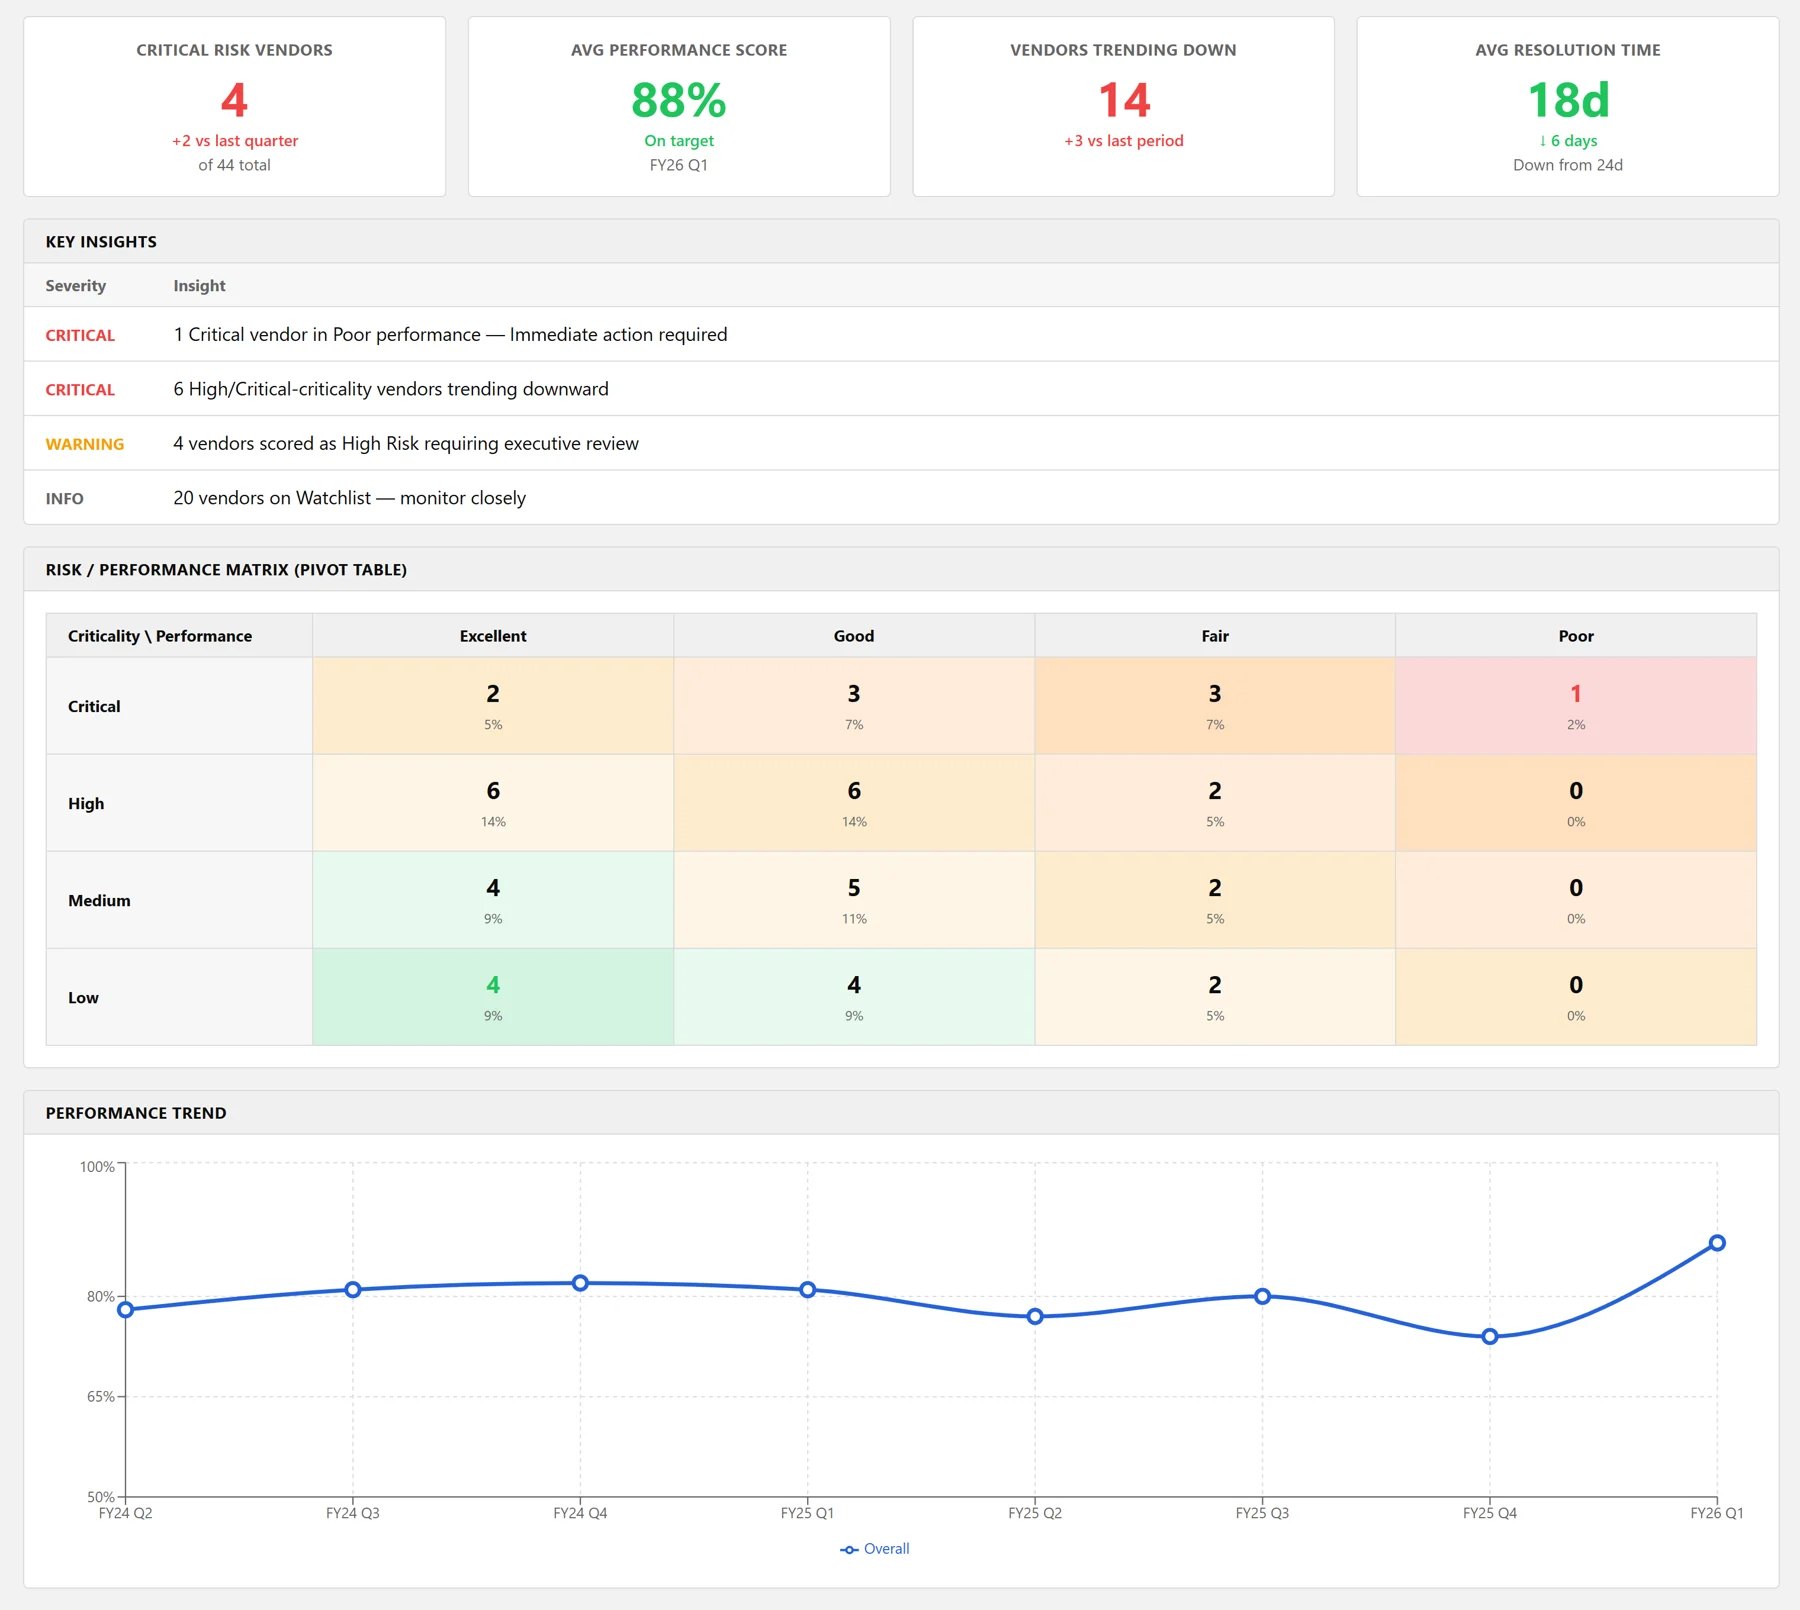
The client plans to expand the policy with notification workflows that alert vendors when a request is approaching the 48-hour threshold, plus reporting dashboards to monitor conversion rates, cycle time, and SLA performance. This continuous improvement loop will further streamline intake and ensure high quality, time-bound evaluations across their portfolio.