Enable
Field faster. Authorization moves when the evidence is already gathered and verified, so your program isn’t waiting on a paperwork cycle.
Cut vendor assessment from 40 hours to two, fix what the assessment finds, and hand your authorizing official documented risk reduction.
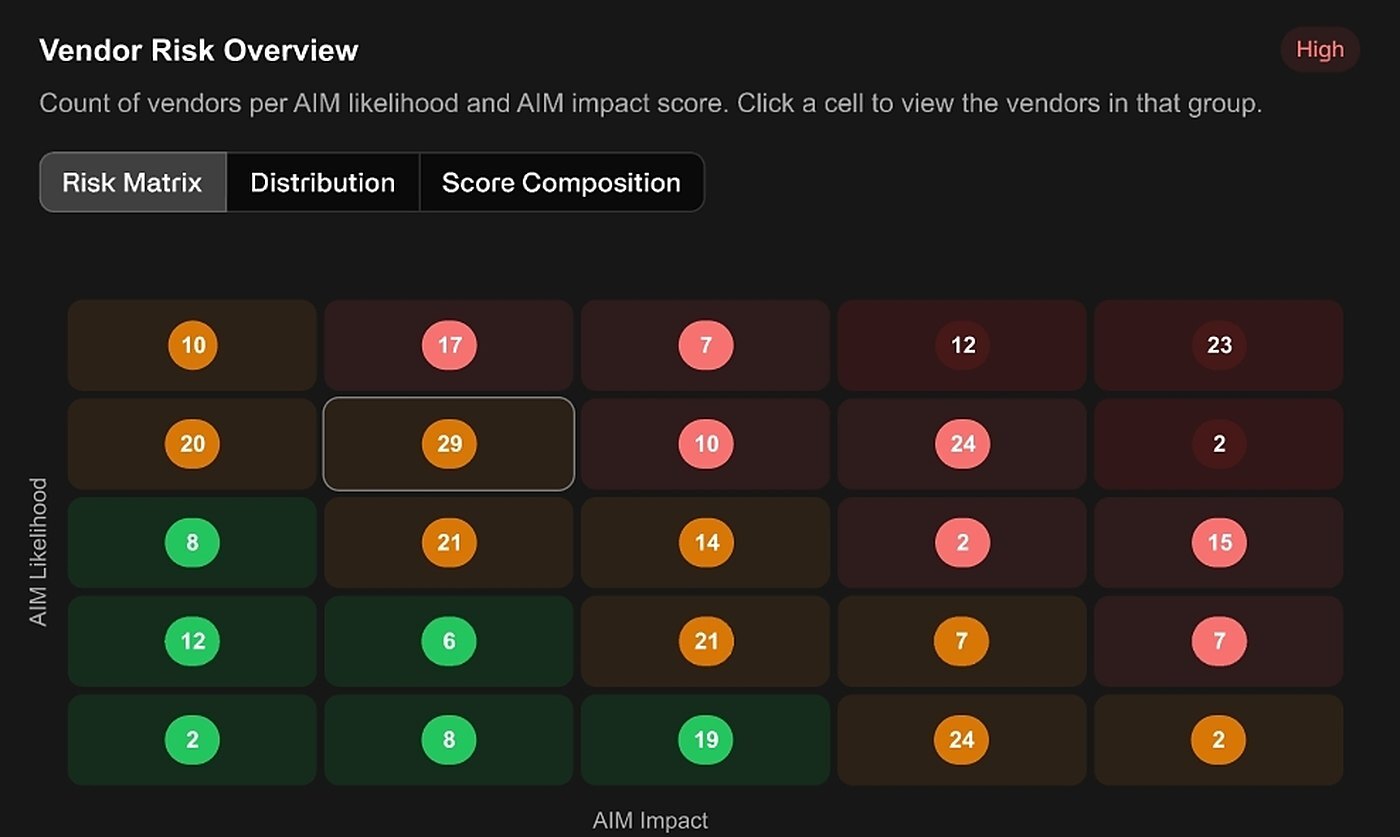
One weapon system carries millions of components, sourced through tiers of suppliers no program office ever put on contract.
Assessment ran at human speed, so most of that population went unassessed. Not by choice. By budget.
Operating at Impact Level 5 and 6, including classified environments
Fortress provides cyber supply chain risk management (C-SCRM) for the Department of War. AI agents assess the vendors, hardware, and software behind fielded systems, and a Fortress analyst reviews anything critical before it reaches a program office.
Our federal team includes former military officers and DoW civilians who ran cyber programs at the command level. We’ve stood up C-SCRM programs for major commands.
Field faster. Authorization moves when the evidence is already gathered and verified, so your program isn’t waiting on a paperwork cycle.
Threats don’t stop at authorization. Monitoring runs continuously, so a supplier that changes hands in March isn’t found at next year’s review.
We take a supplier’s product apart at the component level and check every piece against known vulnerabilities before it’s fielded.
Vendor populations monitored against DoW third-party risk frameworks, with foreign ownership, control, and influence surfaced before procurement.
Learn MoreHardware and software bills of materials analyzed for vulnerabilities, foreign influence, and prohibited components before anything enters your environment.
Learn MoreOne view across vendors, products, and assets, including the nth-tier suppliers no program office ever put on contract.
Learn MoreNew risks surfaced continuously for every vendor, product, and asset, rather than at the next scheduled review.
Learn MoreExposure mapped across your systems in a dashboard your team can brief from, with remediation ranked by what matters most.
Full hardware teardowns paired with open-source intelligence, deconstructing firmware and software to find what no document review would surface.
Every vendor, product, and asset scored against mission criticality, so priority reflects operational impact rather than raw severity.
Risk monitored across design, procurement, and maintenance, so a system stays assessed for as long as it stays fielded.
That authorization covers classified environments. Fortress holds a top-secret facility clearance, and 75% of our government team carries an active one. The people on your program are already read in.
Fortress maps to the frameworks that govern your program and keeps the evidence current, so authorization stops holding up the mission.
Deconstruct hardware and software to identify components, 4th-party relationships, and full bills of materials.
Full alignment with the NIST SP 800-53 Rev. 5 SCRM control family. Documented, auditable, continuously maintained.
Automate evidence collection and control mapping against the secure software requirements the order and memoranda impose.
Identify and close compliance gaps ahead of your next assessment.
Identify 4th-party hardware and software relationships, run FOCI analysis, and flag risks tied to Countries of Concern.
Automated component analysis to identify counterfeits, non-conformances, and prohibited components.
Fortress is available now through established federal vehicles. No sole-source justification. No drawn-out acquisition cycle.
Sole-source, five-year ordering period. Contract N0042125D0086. Open to the Navy, DoD, and affiliated agencies via MIPR or IPAC.
One of four unrestricted seats on the $900M+ SCRIPTS award. BPA 47QTCA25A0005.
Contract 47QTCA24D006Q. Software licenses, subscription services, and IT professional services.
Other Transaction Authority for rapid prototyping and fielding.
Fortress has been an invaluable partner in helping us build and sustain our supply chain risk management program.
Fortress covers your full vendor and component population, then fixes what it finds and documents everything. Your program reaches authorization with the evidence already gathered, and nothing surfaces at inspection you didn’t already know about.
Fortress provides cyber supply chain risk management for Department of War programs. AI agents continuously assess the vendors, hardware, and software behind fielded systems, and analysts validate every critical finding. The platform identifies vulnerabilities, foreign influence, and compliance gaps, then works remediation with the teams who can close them.
Yes. Department of War is the secondary designation authorized for the U.S. Department of Defense. The statutory name remains Department of Defense until Congress changes it. Fortress serves the department under both names, and its contract vehicles are written against the statutory designation.
Yes. Fortress holds Authority to Operate at Impact Level 5 and Impact Level 6, including classified environments, and maintains a top-secret facility clearance. 75% of the Fortress government team holds active security clearances, with personnel cleared up to TS/SCI supporting defense and national security programs.
Fortress is available through a sole-source Navy IDIQ, contract N0042125D0086, with a five-year ordering period open to the Navy, DoW, and affiliated agencies via MIPR or IPAC. Fortress also holds one of four unrestricted seats on the GSA SCRIPTS BPA, plus a GSA MAS Schedule and OTA pathways.
Fortress maps to DoDI 5000.90, NIST SP 800-53 Rev. 5, SP 800-161, and SP 800-171, Executive Order 14028 with OMB Memoranda M-22-18 and M-23-16, CMMC, CYBERSAFE, and NDAA 2019 Section 889. Fortress contributed directly to Executive Order 14028 and leads working groups shaping federal C-SCRM standards.
No. Fortress never uses client data to train AI models, never shares data across tenants, and never exposes it outside the platform. All data is processed in isolated, accredited environments authorized at Impact Level 5 and 6. For defense programs, that is a baseline security requirement.